
Private-network operators
Turn network observations into a clearer view of what went wrong, which actions are appropriate and when an engineer should intervene.
RESEARCH-LED NETWORK INTELLIGENCE
MAVERIC is developing secure AI control for private 5G and Open RAN. We connect network evidence, decision checks and recovery—with operators in control.
RESEARCH & DEVELOPMENT Rooted in research at RPTU · Kaiserslautern, Germany
Observe. Understand. Act safely.
Security before execution.
Recovery with evidence.
Learning with local data.
When equipment, applications and control policies interact, finding a fault is only the beginning. The next challenge is deciding what to change—and knowing that the change helped.
Turn network observations into a clearer view of what went wrong, which actions are appropriate and when an engineer should intervene.
Connect evidence across vendors and define how new intelligence fits into existing management systems and operational workflows.
Translate service interruptions into testable scenarios, so new automation is evaluated against the needs of your operation.
Have a challenge in mind? Let’s explore it together.
AI can help operate complex networks. But an incorrect action, a policy conflict or unreliable data can put live services at risk. MAVERIC brings security, recovery and learning into one coordinated research concept.
SECURE AI CONTROL
Research threat detection and checks on proposed control actions, so safety constraints and operator policies can be considered before a change reaches the network.
AUTONOMOUS SELF-HEALING
Investigate policy conflicts and network instability. Develop recovery actions that respect operator intent, support rollback and explain what changed.
FEDERATED INTELLIGENCE
Research shared model improvement without centralising operational data, with checks for model drift, unreliable updates and safe deployment.
These capabilities are in development. MAVERIC’s current goal is an integrated research demonstrator.
Our proposed architecture connects network observations, decision checks and recovery. The aim is to make every step traceable, from detecting a problem to verifying the outcome of an action.
We’re designing for gradual automation: recommendations first, operator approval where needed, and autonomous actions within defined boundaries.
MAVERIC stands for Modular AI-driven Virtualized Enhancement for RAN Intelligence and Control.
The design combines management and orchestration (SMO), longer-term decisions in the non-real-time RAN Intelligent Controller (Non-RT RIC), and near-real-time control (Near-RT RIC). Modular applications, called rApps and xApps, coordinate through open O-RAN interfaces.
PROPOSED O-RAN INTEGRATION
Deployment, versioning, audit records and recovery authority.
Policy generation, diagnosis, model training and aggregation.
Live telemetry, bounded-latency inference and safety checks on control actions.
Open interfaces · Modular rApps and xApps · Operator-defined policies
FROM OBSERVATION TO VERIFIED OUTCOME
A proposed workflow for the demonstrator. Each action should have supporting evidence, a defined authority and a way to check the result.
Bring together available telemetry, events and network context.
Network observationsInvestigate anomalies and competing explanations for a fault.
Diagnosis & supporting evidenceCheck operator policies, constraints and approval requirements.
Bounded recovery proposalCompare results with the intended outcome; escalate or roll back where needed.
Outcome & audit recordIllustrative settings for future validation—not customer deployments. Each requires a clear service objective and access to relevant network observations.
When connected equipment loses reliable service: investigate network anomalies before proposing changes that could affect production.
When mobile robots experience inconsistent connectivity: examine mobility, performance and competing control policies together.
When campus services depend on connectivity: explore resilient operation and collaborative learning that keeps raw operational data local.
05 / RESEARCH INTO PRACTICE
Our existing foundation is a machine-learning detection application evaluated on a laboratory Open RAN testbed for one family of denial-of-service attacks. This establishes a starting point for research; it does not yet validate the complete MAVERIC system.
The integrated demonstrator is in development. Our goal is to evaluate secure control, recovery and learning together in a realistic environment with equipment from multiple vendors.
EXISTING FOUNDATION
Security detection on a research testbed.
DEVELOPMENT FOCUS
Self-healing and federated intelligence remain at the concept and early experimental stage.
RESEARCH GOAL
A proof of principle tested in a relevant environment, targeting Technology Readiness Level 5.
Selected work co-authored by Prudhvi Kakani on Open RAN security. These publications provide background to our approach; they are not validation of the integrated demonstrator.
XAPP SECURITY · 2024
Research into application vulnerabilities, threats and security approaches in Open RAN.
E2 INTERFACE SECURITY · 2024
Research into security threats and protection approaches for the interface between the controller and radio network.
MAVERIC connects Open RAN security research with the practical questions of operating complex networks. Based in Kaiserslautern, we’re building relationships with operators, integrators and researchers across Europe.
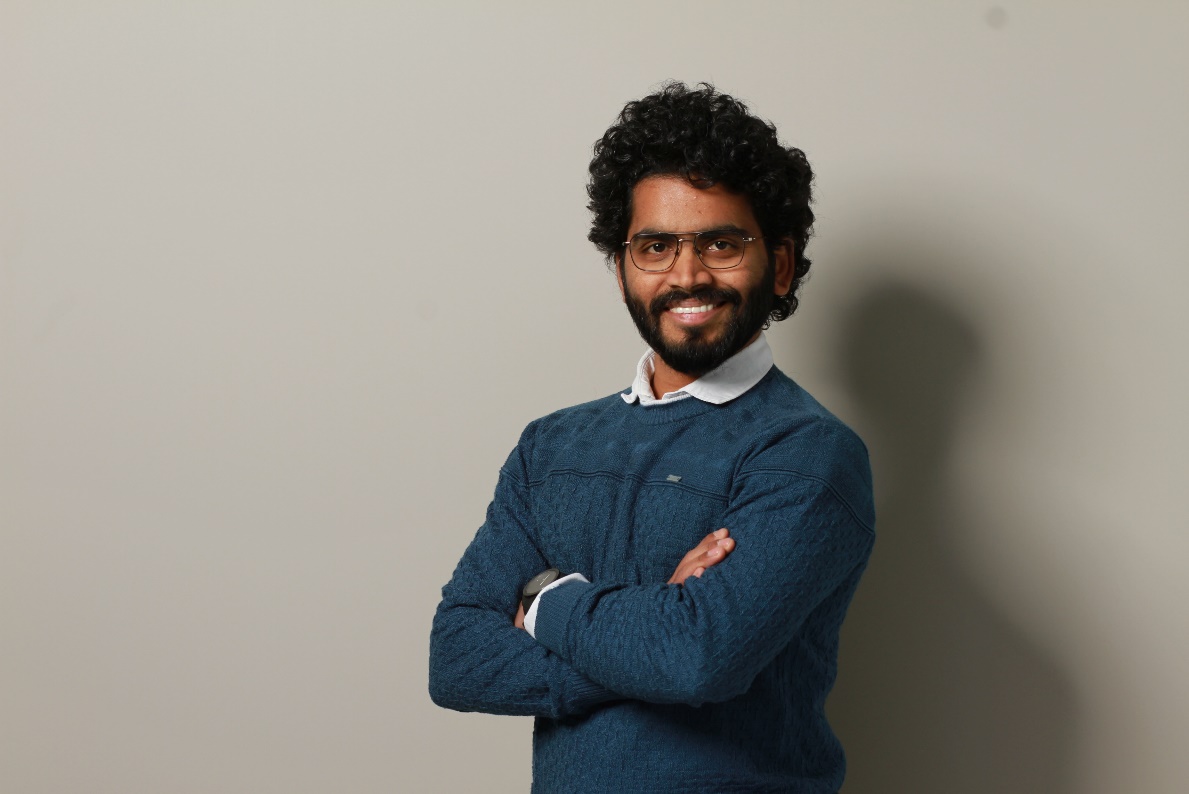
Founder & Product Lead
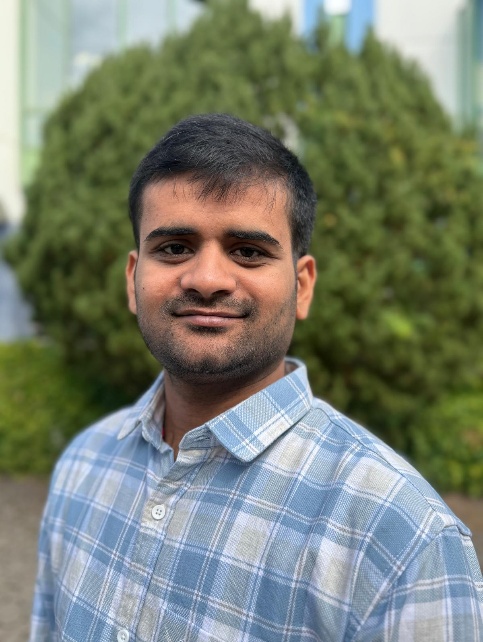
Technical Lead
QUESTIONS, ANSWERED
What to know before we talk.
MAVERIC is a research-led startup initiative. We are developing an integrated demonstrator, rather than offering a production-ready platform. Conversations today focus on operational requirements, integration and potential validation scenarios.
Private-network operators, telecom systems integrators, industrial connectivity teams and research collaborators. A specific recurring fault, difficult diagnosis or concern about automated changes is a useful starting point.
Our proposed approach is to complement existing management and orchestration systems with coordinated security, diagnosis and decision checks. Compatibility will depend on the interfaces, telemetry and control permissions available in each environment.
Our design starts with recommendations and operator oversight. Any future autonomous actions would need explicit boundaries, policy checks and a way to verify the result. The level of automation is part of the research and validation work.
We would first discuss your network environment and an operational challenge. Together, we can assess what observations are available, identify a bounded test scenario and agree how a useful result would be measured. No sensitive network data is needed for the first conversation.
Are you operating a private network, integrating equipment, or exploring trustworthy automation? We’d like to hear what is difficult today and what a useful solution would need to do.
Our ambition is to support European technological sovereignty through open interfaces, operator control and research that can transfer into real deployments.
Useful starting points include time spent diagnosing a fault, unnecessary site visits, or uncertainty about an automated change. Together, we can define what a meaningful improvement would look like.
Tell us your organisation, network environment and the challenge you’d like to discuss.
Trust at the heart
of network autonomy.